Showing posts with label News. Show all posts

Tuesday, September 3, 2013

Official: The next edition of Android is “KitKat,” version 4.4

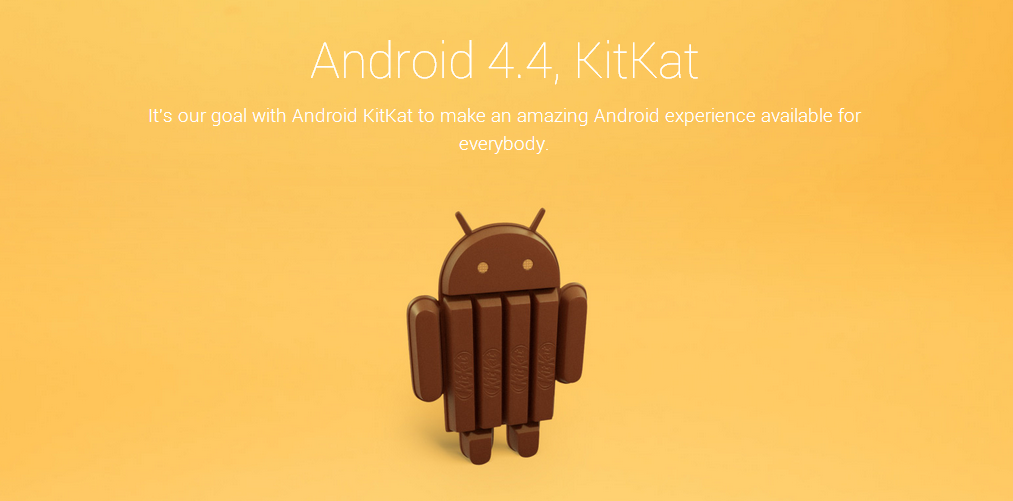
Android-KitKat-640x426

This is not a joke. The next version of Android will be called "KitKat." The above picture is not a photoshop, it's an actual picture shared by Sundar Pichai, the head of Android, on Google+. Google has also launched a website for KitKat at android.com/kitkat/. Right now the site only features a small history of Android and the following announcement:

Android is the operating system that powers over one billion smartphones and tablets. Since these devices make our lives so sweet, each Android version is named after a dessert: Cupcake, Donut, Eclair, Froyo, Gingerbread, Honeycomb, Ice Cream Sandwich, and Jelly Bean. As everybody finds it difficult to stay away from chocolate, we decided to name the next version of Android after one of our favorite chocolate treats, Kitkat®!

Yes, this is an actual cross-branding initiative with Nestle's KitKat. The Android site links back to kitkat.com, and KitKat is celebrating the renaming with a new Facebook Profile picture. Nestle will be releasing a limited edition Android KitKat bar, with Willy Wonka-style winning tickets for a new Nexus 7 or Google Play credits.

For almost a year, the community believed the next version of Android would be called "Key Lime Pie," but apparently Google just loves to keep its fanbase guessing.

2013-09-03_12-56-39-640x316

Enlarge

The bottom of the Android page pegs this version as "4.4" and shows off the official logo. There will no doubt be news about this all day, hopefully including the traditional unpacking video. Stay tuned to Ars and we'll continue update this post or compose another as more information becomes available.

Sysadmin security fail: NSA finds Snowden hijacked officials’ logins

sysadmin

The National Security Agency (NSA) is the font of information security wisdom for the US defense and intelligence communities. But apparently, the NSA's own network security is so weak that a single administrator was able to hijack the credentials of a number of NSA employees with high-level security clearances and use them to download data from the agency's internal networks. That administrator was Edward Snowden.

Under Department of Defense (DOD) Directive 8500.2, the director of the NSA, Gen. Keith Alexander, is tasked with approving all the cryptographic hardware and software used by the DOD. The NSA also provides "information assurance" and information system security engineering services to DOD branches and agencies. And along with the National Institute of Standards and Technology, the NSA maintains the master guide for DOD information security systems: the Information Assurance Technical Framework (IATF).

But in what appears to be a case of "do as I say, not as I do," the NSA's internal IT security schemes allowed Snowden, a contractor sysadmin, to pull off a classic insider attack on the agency. An investigation by NBC found that Snowden had used the digital identities of several upper-level NSA officials to log into NSAnet, the agency's intranet—giving him access to data far beyond the needs of a lowly system administrator.

Attack of the superuser

The systems accessed by Snowden limit access by user role, so he could not have used his own credentials on them without overriding access controls. Officials familiar with the case told NBC that Snowden had obtained the "profiles" of a number of NSA employees that have been identified through forensic examination of logs, finding periods when the employees were traveling but their accounts were still used to access the intranet. If Snowden used administrative privileges to reset their passwords, failed logins might have flagged a problem—but they might have simply been shrugged off as passwords forgotten over vacation.

In order to pull this off without raising alarms, Snowden would have needed access to the full credentials of the users whose identities he borrowed. He would have needed to somehow either gain access to the public key infrastructure (PKI) keys found in their user authentication or he would have needed to override multi-factor authentication to gain access to the systems. He also would have needed to avoid detection by audit logs in making those changes (or delete the record of changes after the fact). He managed to do all of these things, download the content, and get it past the NSA's physical security.

Some or all of this trouble could have been avoided if the NSA had followed its own playbook a bit more closely and used administrative and security best practices that are common across government, the financial industry, and other networks where access control auditing and the non-repudiation of data are mandated by laws, regulations, and the nature of the business. Giving an administrator the ability to gain access to user credentials—and the log systems that monitor changes to those credentials—is a classic bad move in network security. As Oracle points out in its documentation for its Enterprise Manager administration tool, "Giving the same level of access to all systems to all administrators is dangerous." In most sensitive enterprise systems, administrators' access powers are limited to very specific roles to prevent giving them the power to compromise multiple systems, making it more difficult for an insider to attack systems and cover his or her tracks.

In the wake of the Snowden breach, Gen. Alexander announced that the NSA would implement two-person administrative requirements; that's a measure that's been recommended by the IATF for over a decade. "Limits can be placed on each individual’s authorized privileges," the IATF says. "The application and the security features it provides can also partly counter these threats with features such as audit, two-person administrative requirements, and covert access prevention and detection." Covert access prevention and detection would include monitoring login locations and watching for attempts to get at data from ways other than through the approved front-end (such as trying to pull directly from a disk directory instead of going through the intranet server).

Networks classified as secret and above at the DOD are supposed to be protected by layers of intrusion detection and automated auditing systems. Security event information management (SEIM) systems and other internal network monitoring tools can be configured to catch log events that human eyes might miss—like a user from Fort Meade logging in unexpectedly from a station in Hawaii. A number of SEIM systems are used by organizations within the DOD for security auditing.

But based on statements by Gen. Alexander and reports about the breach, it appears that the NSA—the agency responsible for monitoring the networks of the world—didn't have a great deal of automated monitoring inside its own firewalls. Instead of using automated systems, the NSA apparently depends on an army of system administrators for its internal defenses—administrators like Edward Snowden. With masses of log data to check through, Snowden likely slipped past the eyes of other administrators or managed to delete or alter log records before they raised suspicion.

The NSA reportedly still doesn't know the extent of what Snowden extracted from the agency's intranet, and investigators are poring over access logs to try to find conflicts that would indicate which users' accounts Snowden used. Given the apparent superuser powers Snowden was able to wield—and the apparent lack of insider threat protection the agency had in place—they may never fully know.

“How can they be so good?”: The strange story of Skype

125252146_042c71ac0c_o-640x480

"I don't care about Skype!" millionaire Jaan Tallinn tells me, taking off his blue sunglasses and finding a seat at a cozy open-air restaurant in the old town of Tallinn, Estonia. "The technology is 10 years old—that's an eternity when it comes to the Internet Age. Besides, I have more important things going on now."

Tallinn has five children, and he calls Skype his sixth. So why does he no longer care about his creation?

On August 29, 2003, Skype went live for the first time. By 2012, according to Telegeography, Skype accounted for a whopping 167 billion minutes of cross-border voice and video calling in a year—which itself was a stunning 44 percent growth over 2011. That increase in minutes was "more than twice that achieved by all international carriers in the world, combined." That is to say, Skype today poses a serious threat to the largest telcos on the planet. It also made Jaan Tallinn and other early Skypers rich.

But something changed along the way. Skype is no longer the upstart that refused to put signs on its offices, that dodged international lawyers, and that kept a kiddie pool in the boardroom. This is the real story of how a global brand truly began, told in more detail than ever before by those who launched it.

The roots of Skype... lie in a simple space driving game?

In the year 2000...

In 2000, as dot-com fever swept America, an entertainment and news portal called Everyday.com brought together a sextet of European revolutionaries.

It began with two people from the Swedish telecom Tele2—a Swede named Niklas Zennström and a Dane named Janus Friis. Zennström was Tele2 employee no. 23; Friis worked his way up in customer service for a Danish operator.

The Swedish owner of Tele2, Jan Stenbeck, was determined to launch the Everyday portal and launch it quickly. As the Swedes were having trouble, Stefan Öberg, the Marketing Director in Tele2's Estonian office, proposed finding some Estonians for the job. In May 1999, Tele2 published an ad in a daily newspaper calling for competent programmers and offering the hefty sum of 5,000 Estonian kroons (about $330) a day—more than an average Estonian earned in a month at the time.

The work went to Jaan Tallinn, Ahti Heinla, and Priit Kasesalu—Estonian schoolmates and tech fans. They had been into Fidonet, a computer network which preceded the Internet, since the Soviet era. They started a small company, Bluemoon, which made computer games such as Kosmonaut. (In 1989, Kosmonaut became the first Estonian game to be sold abroad.) The game earned its creators $5,000 dollars, which at the time was a large sum for any Estonian. But by the turn of the century, the three friends were down to their last penny and Bluemoon was facing bankruptcy.

Short of money, they applied for and got the Tele2 job. The PHP programming language needed for the work was new to them, but the team learned it in a weekend and completed their test assignment much faster than Tele2 requested.

The last of the Skype sextet, Toivo Annus, was hired in Tallinn to manage the development of Everyday.com. The site would soon be complete, with Zennström and Friis working in Luxembourg and Amsterdam, and Annus and the Bluemoon trio working from Tallinn.

Tele2 was thrilled with the Estonians, but the Everyday.com portal failed commercially. Zennström and Friis left Tele2 and lived in Amsterdam for a while. The homeless Friis stayed in Zennström's guest room, and they turned the kitchen into a temporary office.

Together, Zennström and Friis pored over new business ideas. As the US was fascinated at the time with the scandal surrounding Napster, Zennström and Friis planned something similar. But where Napster infuriated the music and movie industries, Zennström and Friis hoped to cooperate with them. They didn't have the slightest doubt about where their new product should be created—in Tallinn, obviously. Kazaa was born.

Kazaa

Kazaa's P2P file-sharing program allowed files to be transferred directly from one computer to another without an intermediary server, thus solving one of Napster's problems. Jaan Tallinn developed the program in a nine-floor, Soviet-style brick building on Sõpruse Puiestee in the Tallinn suburb of Mustamäe. The apartment was actually Jaan Tallinn's home, and at the time, Tallinn was a work-at-home dad. (He only sold the apartment in 2012 and told me that he contemplated attaching a memorial plaque to the wall stating, "Kazaa was created here.")

Kazaa, ready for service in September 2000, swiftly became the most downloaded program on the Internet. The service picked up users at the rate of one per second. Heinla, Tallinn, and Kasesalu were sipping fine wine in their headquarters and thinking, "So this is what it feels like to have half of the world's Internet traffic go through your software."

But on the business side, Zennström and Friis failed to seal a deal with US film and music companies. Kazaa was sued for enabling piracy. "Stolen" music, films, and pornography were being distributed via the application, and the Kazaa owners soon found themselves hiding from an army of ferocious US lawyers.

Zennström repeatedly dodged court summons. One time, he went to see a play at a Stockholm theater and was approached by a stranger. The individual handed Zennström's wife a bunch of flowers and held out an envelope containing a summons for Zennström. The Swede made a run for it; the summons failed to be duly delivered. He was similarly pursued in London, this time by a motorcycle, but service again failed.

When Zennström went to Tallinn for visits with his team, he did so by ferry as he was too scared to fly (by now he's clearly gotten over this, as he owns a private jet and all). And once there, he remained nervous about visitors. "When someone came in through the door and we weren't certain who it was, Niklas would hide under the table," an Estonian coworker reminisced.

The Bluemoon boys began encrypting all of their correspondence and their hard drives. E-mails were not stored for longer than six months. No one wanted to know more than they absolutely needed to know. Zennström changed his phone number as often as he changed his socks.

Charges were never pressed against the coders Heinla, Tallinn, and Kasesalu, but they were involved in the Kazaa proceedings as "an important source of information." A California court requested that the men be questioned and that business secrets concerning Kazaa be confiscated. At first the Estonian government rejected the request, but after a second appeal, the trio was interrogated in the presence of US lawyers.

For the Estonians, the Kazaa proceedings were like playing with fire—a little dangerous but still exciting—and their names began to pop up in the international press.

Afraid of being arrested, Zennström and Friis avoided flying to the US for several years, even though Kazaa had been promptly sold (at least on paper) to Australian businessmen, and its headquarters had been moved to the island nation of Vanuatu. The duo failed to make peace with the US for several years, and their ultimate redemption cost Friis and Zennström big money. The two eventually contributed to a more than $100 million payout for the music and movie industries.

Verizon buys itself from Vodafone for $130 billion

Verizon

America's largest mobile phone carrier Verizon Communications announced yesterday that is was buying out British firm's Vodafone 45 percent stake in the company for US$130 billion. The deal will give Verizon 100 percent ownership in the company. Until the buyout yesterday, Vodafone had owned its 45 percent stake for over a decade.

While complete ownership of the company will give Verizon more leeway to do what it wants, Vodafone's ownership didn't have a lot to say about the direction of the carrier since it had owned less than half the company. Verizon says it will focus on rolling out 4G to more areas of the country. As for Vodafone, now that they are cash-rich, the company plans to spend at least £6 billion speeding up 4G roll out in the UK and also improve fiber optic broadband speeds to homes.

Tuesday, August 27, 2013

Facebook Wants to Give Internet to 5 Billion People


Mark Zuckerberg has a dream. And if we’ve learned anything from the ‘Social Network’ is that what the Facebook founder wants, the Facebook founder gets.

This time, Zuckerberg wants to give Internet to 5 billion people. Just imagine how many new Facebook users that means.

Joking aside, and trying to ignore the profit such an enterprise could bring, Facebook has actually teamed up with several tech giants to set up Internet.org, an organization whose main target is to bring the WWW to those parts of the world that still don’t have access to it. Other founding members include Ericsson, MediaTek, Nokia, Opera, Qualcomm and Samsung, among others.

Facebook Wants to Give Internet to 5 Billion People
The organization names three major lines of action to reach their goals of offering widespread Internet access as a means to boost social, economic and political development and contribute to humankind progress, according to a UN Human Rights Council quote posted on the Internet.org website.

The first step is to make Internet access more affordable, possibly by using high quality, yet lower cost smartphones. The second step is to use data in a more efficient manner; more specifically, to reduce the amount of data most Internet applications require, and one way to achieve this is by improving the infrastructure.  And the third step would be to bring in businesses that would support the project by offering them incentives.

One can’t ignore that this is quite an ambitious plan, even if it is far from being an altruistic one. All the companies involved, Facebook included, would benefit from bringing Internet to 5 billion people. According to the group, only a little over one third of the world’s population, 2.7 billion people have Internet access at the moment.

In an interview with CNN, Zuckerberg insisted that connectivity is a human right and would offer people access to things such as healthcare and information about their country’s state of affairs, ultimately helping them decide what sort of government they want.
Which is truly admirable, but it will take a lot of time until the plan can become reality, according to analysts. One of the major issues that the Internet.org initiative will have to overcome is the lack of a constant electricity supply in most developing countries that the program is targeting. Other problems include the lack of proper infrastructure, poverty and illiteracy.
In other words, all those billions of new Facebook users won’t be able to share much and tag themselves in photos if they can’t read or only have enough electricity to check their feed only a couple of times per week.

So overall, the Internet.org plan to bring Internet to 5 billion people is a good idea, but unlikely to happen any time soon. What do you think of the initiative? Should the tech giants behind it focus on other priority issues for the developing world before going ahead with the connectivity idea?

[Image via under30ceo]
 
Blogger TemplateAnyThingOnCloud © 2013. All Rights Reserved. Powered by Blogger
Top